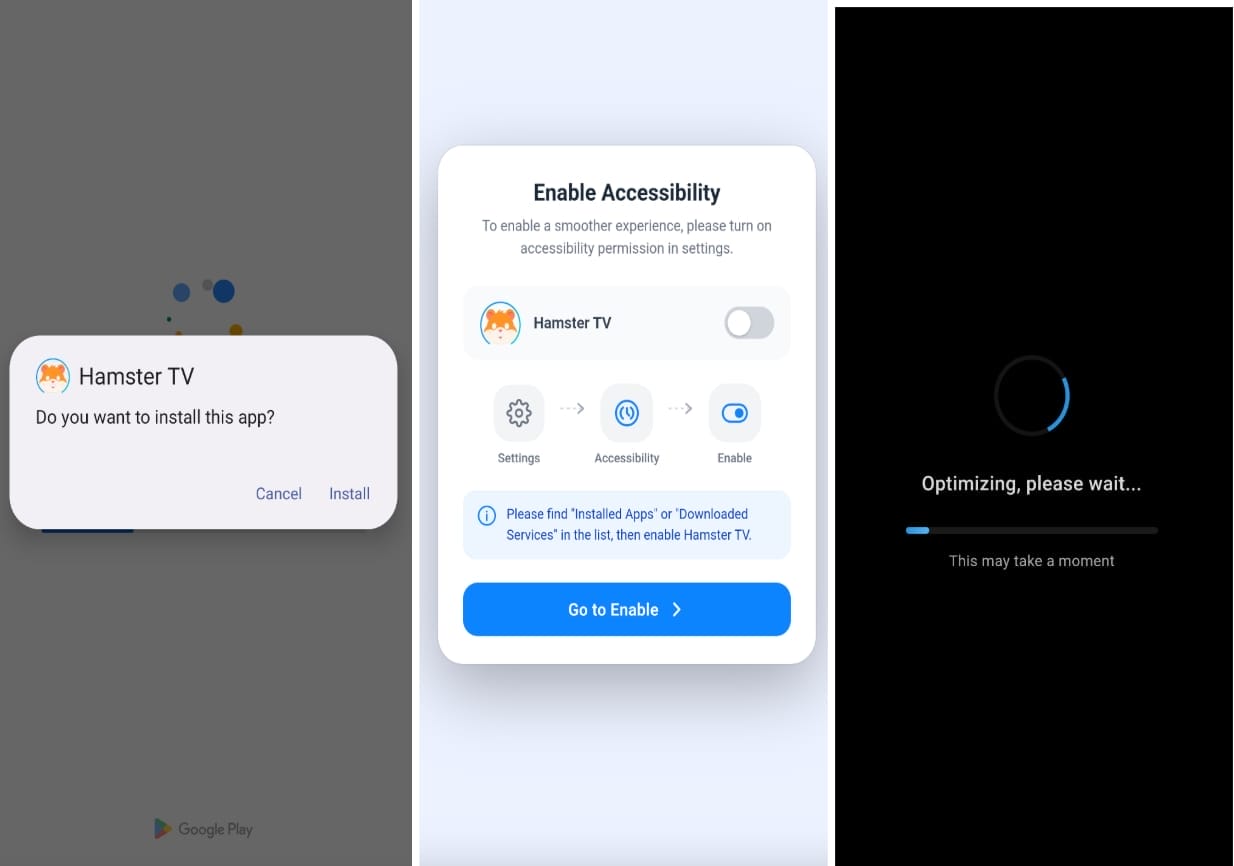
The Android malware known as ToxicPanda has updated its capabilities, now focusing on 349 applications and supporting 167 remote commands. This new version, referred to as ToxicPanda 2.0, requests VPN service permissions to create a local network interface, allowing it to control the traffic that passes through it. This feature enables the malware to block communication from Google Play and Google Play Services.
By controlling the network traffic, ToxicPanda can interfere with security checks and actions such as app verifications, updates, and Play Protect communications. After blocking Google Play, the malware proceeds to extract and install its payload, and then requests Accessibility Service permissions to further compromise the device.
According to the mobile security firm Zimperium, ToxicPanda 2.0 is distributed through Amazon AWS-hosted buckets. The malware now includes functions to automate the Android Wireless Debugging Bridge (ADB), granting shell-level access to infected devices. This version supports 167 commands and phishing overlays for 349 banking, financial, cryptocurrency, and e-wallet apps, targeting users in 16 countries.
Abusing ADB
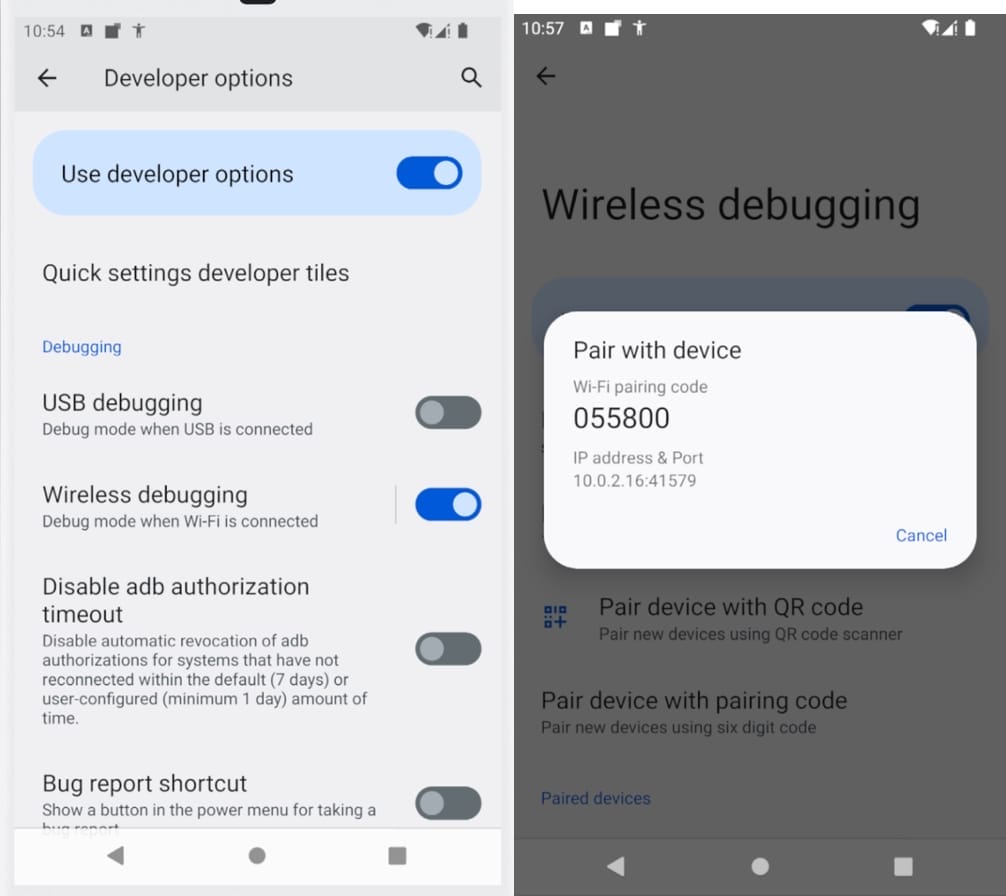
One notable feature in the recent ToxicPanda variants is the automatic abuse of the Android Debug Bridge to gain shell access. ADB is a command-line tool for executing shell commands on Android devices. Wireless ADB, introduced in Android 11, allows this access over Wi-Fi without a USB connection. Using Accessibility Services permissions, the malware enables Developer Options, activates Wireless Debugging, extracts the six-digit pairing code and port, and connects with the device's local ADB service.
Once the malware gains shell user permissions, it starts executing high-privilege commands directly through the ADB daemon, the malware bypasses standard Android runtime consent prompts to grant itself broad permissions, neutralize OS background restrictions, silently enable critical components, and enforce persistence, Zimperium explains.
The abuse of Wireless ADB is a growing trend in Android malware, with other malicious tools implementing similar mechanisms. For example, Group-IB recently reported that the latest version of the RedHook malware also uses Wireless ADB for shell access. Zimperium has published a list of indicators of compromise (IoCs) for the latest ToxicPanda version on its GitHub repository.
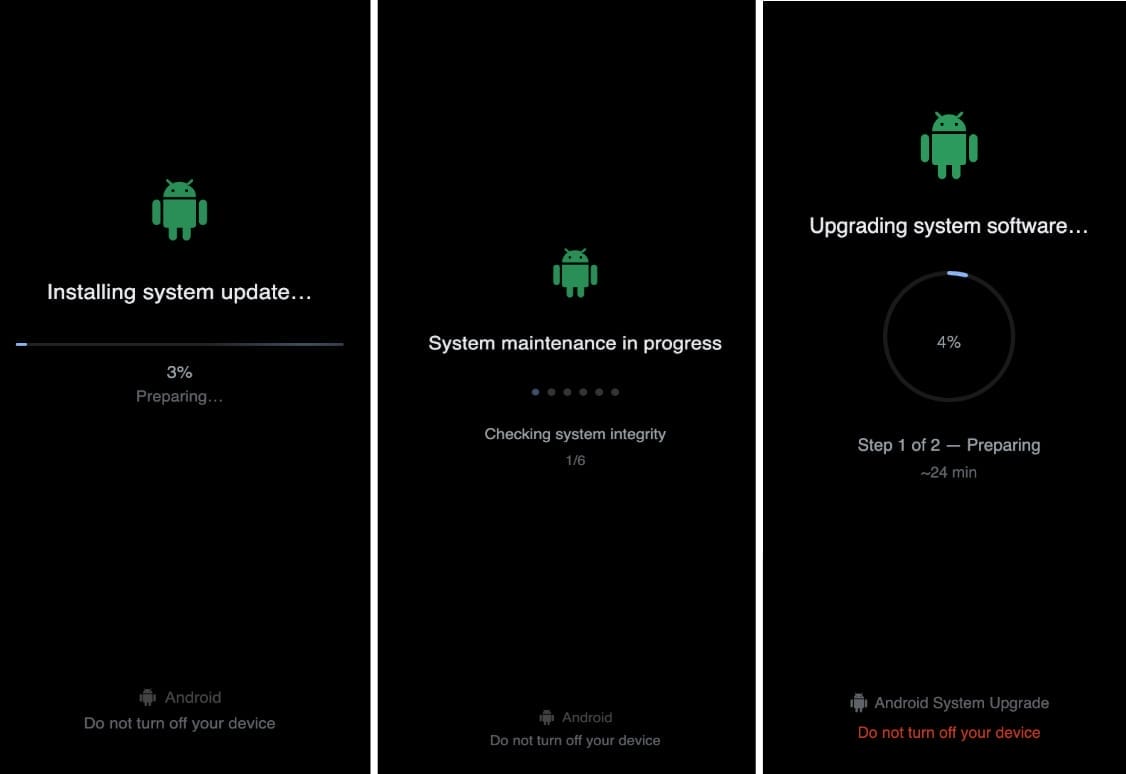
ToxicPanda also includes a separate PIN-harvesting module targeting 140 financial and cryptocurrency apps, and can dynamically update its target list. The malware overlays invisible screens on top of legitimate apps to capture touch inputs, and spoofs the Android lock screen to steal device PINs, patterns, and passwords. Some samples also show fake system update screens to hide malicious activities while they run.
The command 'autoBoot' identifies the device manufacturer and triggers the corresponding OEM-specific auto-start or power management settings to maintain persistence. Zimperium notes that this bypasses battery consumption protections that kill background processes on Xiaomi, OPPO, Vivo, Samsung, and Huawei devices.